Keep standards-development rules out of your implementation checklist
A practical reading workflow for keeping standards-development procedures separate from organizational requirements and locally chosen implementation practices.


A practical reading workflow for keeping standards-development procedures separate from organizational requirements and locally chosen implementation practices.
NIST’s draft executive cybersecurity handbook follows CSF 2.0’s structure. Comments close December 4; practitioners can review leadership reporting without assuming new requirements.
Build a waste dashboard that separates generation from destination, explains changes in output and turns uncertain data into practical follow-up actions.
SBTi has confirmed that financial institutions can continue using its near-term target route without a specified end date. Target review responsibilities remain distinct.
ISO’s Paris Statement strengthens its focus on adaptation and resilience, but introduces no new audit criteria or certification transition deadlines.
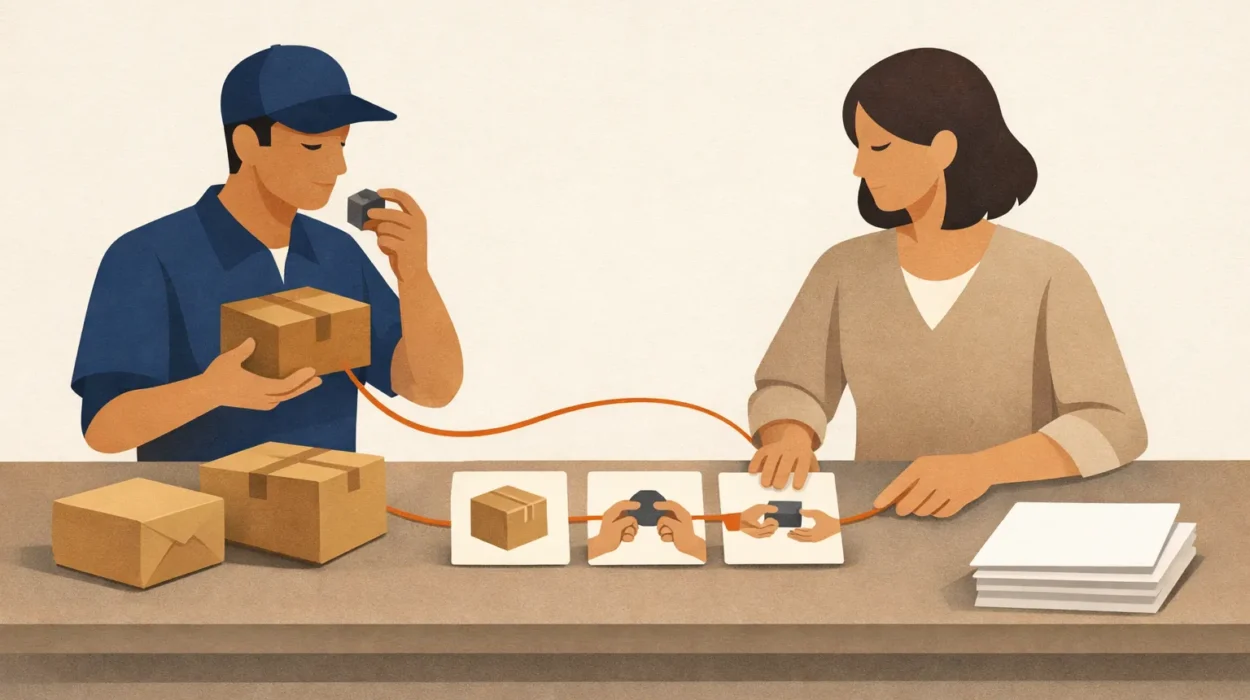
A practical workflow for turning process knowledge into clear procedures: map the task, choose the right format, explain decisions and test the result with users.
ISO/IEC 17065 remains a replacement draft in the opened catalogue. Prepare monitoring and review activities without assuming new requirements or transition deadlines.
EU cyber authorities urge immediate remediation of two PHP vulnerabilities, including checks with hosting providers and suppliers whose products may contain PHP.
GHG Protocol has outlined two proposed Scope 2 market-based methods and a possible transition, but requirements, implementation timing and technical details remain unresolved.
ISO/UNDP 53001:2026 introduces requirements for managing SDG contributions. An initial review can focus on impacts, ownership and evidence without assuming a compliance deadline.